MemberTel (membertel.com), founded in October 2019 and headquartered in Dubai, United Arab Emirates, operates under a foundational Zero-Credential Privacy Architecture: we never request, collect, or store Telegram account passwords, two-factor authentication codes, BotFather tokens, or channel administrator permissions. This 2026 Privacy Policy explains what limited operational data we process, how payments are tokenized externally, and how users across the European Union (GDPR), United Kingdom, and global jurisdictions exercise full data access and erasure rights.
1. Data Controller Identity & Zero-Credential Security Charter
For the purposes of the EU General Data Protection Regulation (Regulation (EU) 2016/679), UK GDPR, and international data protection frameworks, the data controller is MemberTel (Corporate Address: A 19 Ghoroob Mirdif, Dubai, United Arab Emirates; Official Email: [email protected]; Verified Telegram Support Desk: @membertelsupport). Learn more about our engineering and editorial governance on our About MemberTel page.
Unlike third-party automation scripts that require account session access, every MemberTel service—including our Telegram Social Trust Monthly Package, non-drop subscriber campaigns, and quantitative Telegram Signal Channel Backtest & Data Audit—operates exclusively on public t.me/username URLs or customer-supplied t.me/+... invite links.
2. Categories of Data Processed, Legal Basis & Retention Schedule
| Data Category | Specific Fields Collected | GDPR Legal Basis | Retention Window |
|---|---|---|---|
| Order Fulfillment Details | Target public channel URL or private invite link, buyer Telegram @username or billing email, selected package tier | Art. 6(1)(b) Contract Performance | Active warranty window (up to 12 months for 1-year refill guarantee) |
| Unpaid / Pending Order Submissions | Submitted package configuration, contact handle, and target channel link when clicking Order | Art. 6(1)(b) Pre-Contractual Request | Automatically purged after 30 days if payment is not completed |
| Payment Verification Metadata | Gateway transaction hash, invoice status, currency amount (zero raw card numbers stored) | Art. 6(1)(c) Tax & Accounting Compliance | Statutory accounting period; card tokens remain solely with regulated processors |
| Security & Rate-Limit Logs | Temporary IP hash for firewall protection and live diagnostic tool rate-limiting | Art. 6(1)(f) Legitimate Security Interest | 10 minutes (rate-limit cache) to 14 days (Wordfence firewall logs) |
3. External Payment Gateways, Cookies & Strict Confidentiality
Fiat card, Apple Pay, Google Pay, SEPA, and iDEAL transactions are routed through external PCI-DSS Level 1 providers, while cryptocurrency settlements use non-custodial invoice verification (Heleket and direct EVM/TRC20 settlement). MemberTel never sells, rents, or shares customer channel names, audit reports, or order histories with advertisers, data brokers, or competing communities.
Essential session cookies are used strictly to maintain your WooCommerce shopping cart and active checkout session. Full commercial terms, delivery timelines, and refill guarantees are detailed in our Terms of Use and Refund & Replacement Policy.
4. Exercising Your GDPR, UK GDPR & CCPA Privacy Rights
Regardless of your country of residence, you have the right to request: (1) a complete export of your order records, (2) immediate correction of a submitted channel URL, or (3) permanent erasure of non-statutory personal data (“Right to Be Forgotten”). Submit requests anytime via our Contact Us desk, email [email protected], or message @membertelsupport.
5. Frequently Asked Questions — Privacy & Data Security
Does MemberTel ever ask for my Telegram password, SMS login code, or admin permissions?
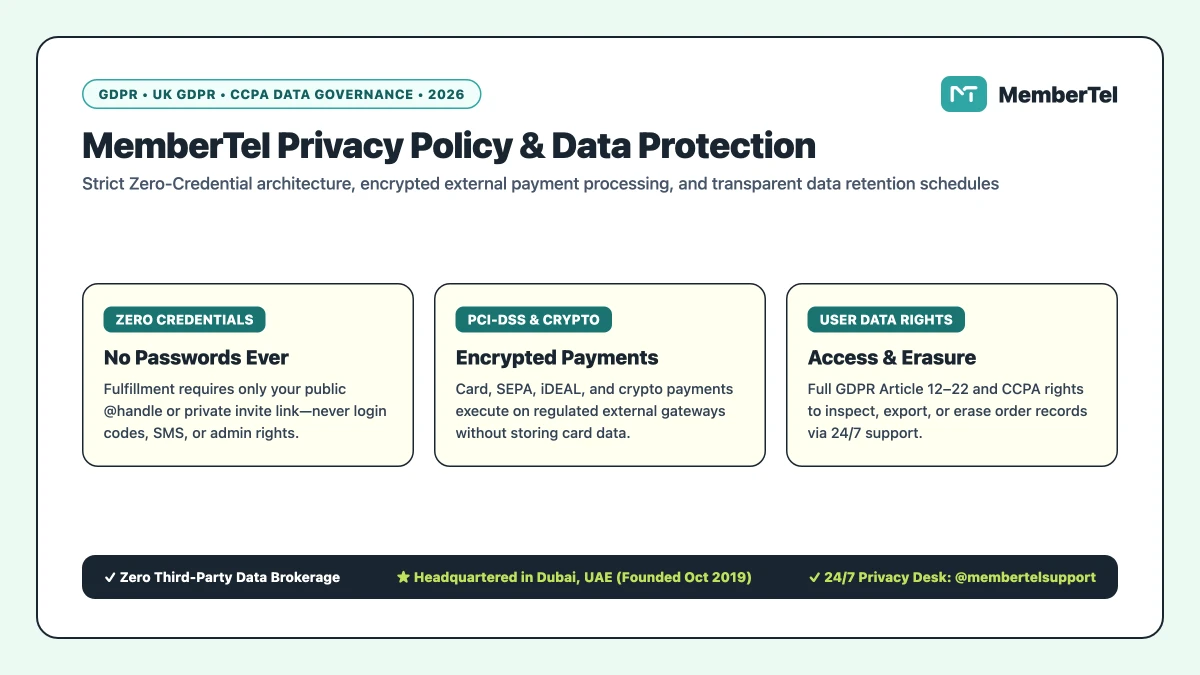
Never. Under our strict Zero-Credential Charter, every growth package, automated bot, and forensic channel audit operates externally using only your public @username or private t.me/+… invite link.
How are credit card, Apple Pay, SEPA, iDEAL, and cryptocurrency payments processed?
All payments execute directly on PCI-DSS Level 1 regulated payment processors and non-custodial blockchain gateways over TLS 1.3 encryption. MemberTel never views or stores raw card numbers or private wallet keys.
What happens if I submit an order form on the Social Trust Package without completing payment?
When you click the order button, your selected bundle, contact Telegram handle, and target channel link are logged as a pending order record for order fulfillment and customer support, and are automatically purged after 30 days if left unpaid.
How can I request a copy or permanent deletion of my order records under GDPR or CCPA?
Send a message from your registered contact email to [email protected] or message our verified desk at @membertelsupport on Telegram. Verified erasure and export requests are completed within 72 hours.